
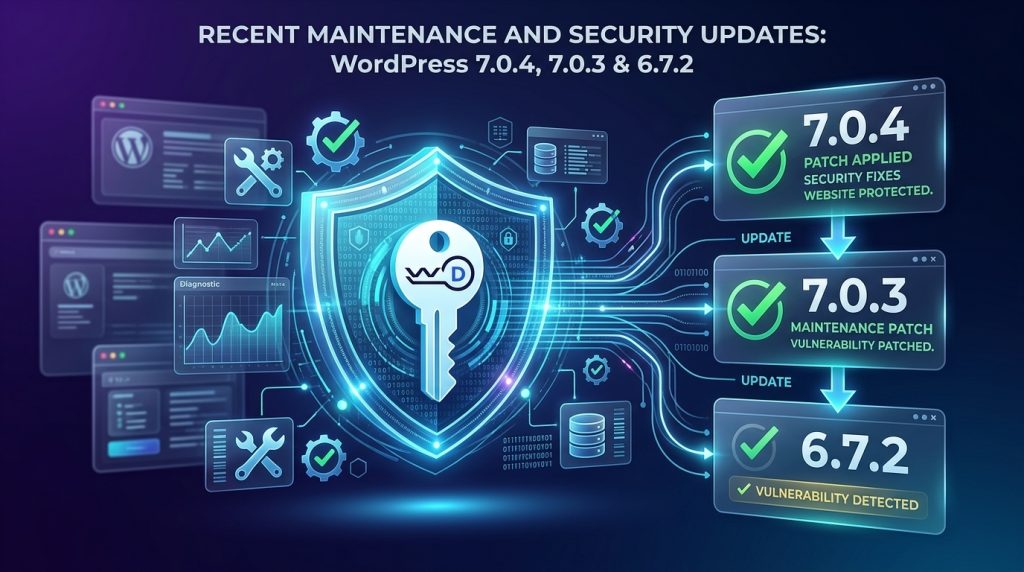
1. Critical Security & Maintenance Releases: What You Must Know
┌────────────────────────────────────────────────────────┐
│               RECENT CRITICAL RELEASE MATRIX           │
├────────────────────────────────────────────────────────┤
│ • WordPress 7.0.4  ► Patches High-Severity RCE Flaw    │
│ • WordPress 7.0.3  ► Neutralizes Login Screen XSS      │
│ • WordPress 6.7.2  ► 35 Core Bug Fixes for Legacy Stacks│
└───────────────────────────┬────────────────────────────┘
                            │  Compounding Exposure Risk
                            ▼
┌────────────────────────────────────────────────────────┐
│           PROACTIVE SANDBOXED STAGING PROTOCOL         │
│ Code Validation • Zero Live Downtime • Database Backup │
└────────────────────────────────────────────────────────┘
WordPress 7.0.4 (Released August 12, 2026)
WordPress 7.0.3 (Released August 6, 2026)
WordPress 6.7.2 Maintenance Rollout
2. Key Developer Architecture: AI Connectors & Accessibility Standards
Beyond urgent security patches, the underlying platform architecture continues to evolve with substantial enhancements for developers building modern digital products.
Standardized WP AI Client & Multi-Model Connectors
Unified API Hooks
Developers no longer need disconnected third-party wrappers to connect large language models. The standardized client natively orchestrates API calls, token caching, and prompt pipelines.
Multi-Provider Support
Standardized connectors are actively optimized for industry-leading providers, including OpenAI, Anthropic, and Google.
Enterprise Extensibility
Teams can build custom content generation, automated taxonomy tagging, and semantic vector search features natively within theme.json and block register APIs.
Administrative Accessibility Adjustments
If your team utilizes older custom administrative plugins or bespoke dashboard portals, these accessibility refinements may alter DOM rendering. We recommend running targeted compatibility audits on custom admin tooling to prevent workflow disruptions.
3. Code Architecture: Defensive Execution & AI Connection Wrapper
PHP
<?php
/**
* Corporate AI Connector Telemetry Guard
* Programmatically wraps third-party model requests within non-blocking execution gates
* to protect server resources and maintain sub-second TTFB.
*
* Engineered for Enterprise Platforms – WPDepartment.com
*/
if ( ! defined( ‘ABSPATH’ ) ) {
exit;
}
add_action( ‘wp_ajax_execute_sovereign_ai_handshake’, ‘wpd_safe_ai_connector_dispatch’ );
function wpd_safe_ai_connector_dispatch() {
// 1. Verify administrative nonce and capabilities
check_ajax_referer( ‘wpd_ai_security_nonce’, ‘security’ );
if ( ! current_user_can( ‘edit_posts’ ) ) {
wp_send_json_error( [ ‘message’ => ‘Unauthorized access’ ], 403 );
}
$prompt_payload = sanitize_text_field( $_POST[‘prompt’] ?? ” );
/**
* 2. Defensive Timeout Window
* Cap model latency to 3 seconds. If the external provider lags,
* fail gracefully without exhausting server execution threads.
*/
try {
$connector_endpoint = apply_filters( ‘wp_ai_client_endpoint’, ‘https://api.connector.internal/v1/generate’ );
$response = wp_remote_post( $connector_endpoint, [
‘timeout’ => 3,
‘blocking’ => true,
‘headers’ => [
‘Content-Type’ => ‘application/json’,
‘X-WP-Client’ => ‘Standardized-Core-v7’
],
‘body’ => wp_json_encode( [ ‘prompt’ => $prompt_payload ] )
]);
if ( is_wp_error( $response ) ) {
throw new Exception( $response->get_error_message() );
}
$body = wp_remote_retrieve_body( $response );
wp_send_json_success( json_decode( $body, true ) );
} catch ( Exception $e ) {
error_log( ‘[AI CONNECTOR WARNING] Model response bypassed: ‘ . $e->getMessage() );
wp_send_json_error( [ ‘message’ => ‘Connection timed out safely.’ ], 504 );
}
}
4. The Staged Upgrade Imperative: Why Direct Live Updates Fail
When a critical vulnerability like the 7.0.4 RCE exploit is announced, the immediate instinct is to click “Update Now” directly on your live site.
However, updating complex corporate platforms on production servers introduces severe risks:
Uncaught Plugin Collisions
A security patch may alter core functions relied upon by older checkout or membership plugins.
Database Deadlocks
Large tables undergoing schema updates during peak traffic can lock the MySQL engine, causing 502 Bad Gateway errors.
Unmonitored Layout Regression
Styling adjustments or script changes can silently break lead capture forms and conversion flows.
Frequently Asked Questions
Shield Your Digital Infrastructure Today
To understand the company behind these solutions, you can explore Staxtar’s official platform for more technical and business details.




